


Data Manager Resists Password Policy After Years of Laxity
Modernizing a password policy is often a thankless task for IT administrators, especially in environments where convenience has long eclipsed security. After a catastrophic ransomware event took a UK school’s network offline for three months, a newly hired IT manager named Daniel attempted to enforce basic security protocols. He discovered that the school’s previous password policy was essentially non-existent, featuring only a six-character requirement that had not been updated for years. This environment created the perfect conditions for unauthorized access and future breaches.
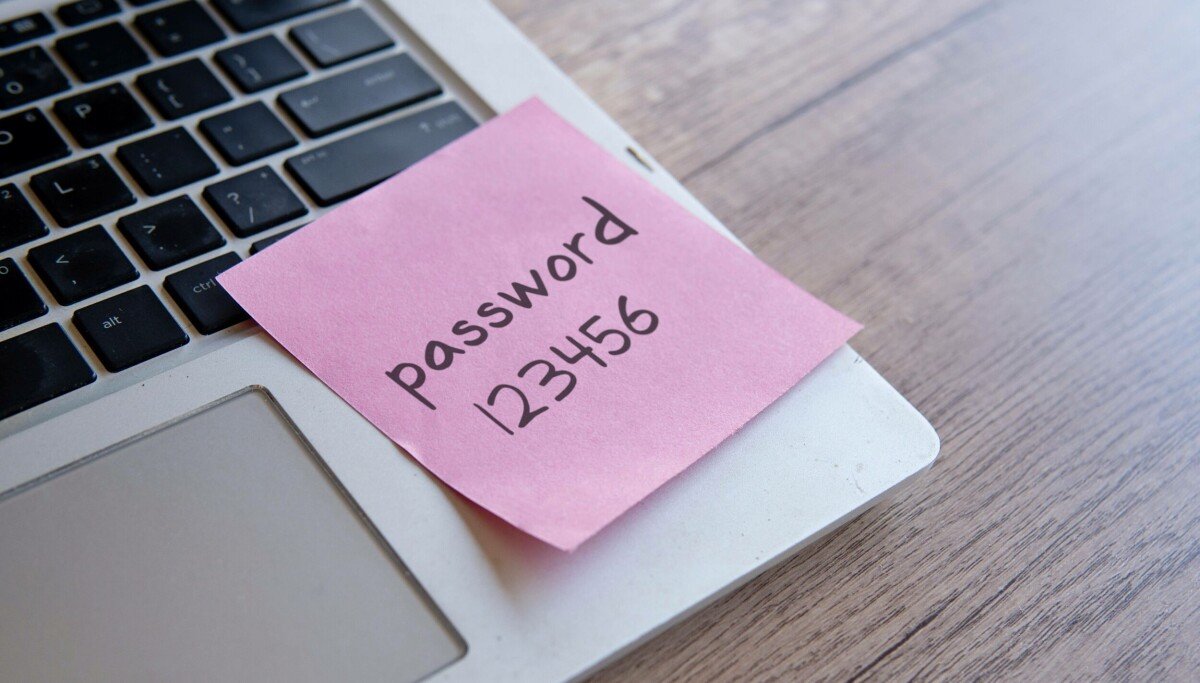
Consequently, the school’s data manager became the primary source of friction. She had utilized the same simple password, ‘letmein’, since 1998 and kept it visible on a sticky note at her desk. When confronted, she argued that keeping the password public was a feature, not a bug, as it allowed colleagues to access her reports whenever she was away. This mindset illustrates a critical failure in understanding how a proper password policy functions to protect institutional assets. Despite the clear risks, she refused to adopt a unique, secure credential, viewing the change as a personal inconvenience rather than a necessary defense.
Leadership Shifts Support The Password Policy
Initially, the school principal buckled under the backlash from staff, commanding Daniel to abandon the new security measures. This retreat created a precarious situation where the IT manager was forced to operate a network he knew was fundamentally broken. However, the situation changed significantly when a nonprofit organization took over management of the school. The new leadership understood that a functional password policy was non-negotiable for an educational institution handling sensitive data. They fully empowered the IT team to reinstate the security upgrades that had been previously blocked.
Moreover, the shift in leadership provided the leverage needed to overcome the remaining resistance. Faced with the reality that she would finally have to learn modern systems and adhere to a strict password policy, the data manager opted for early retirement. This outcome allowed the school to move forward with a much more resilient network architecture. Ultimately, the story serves as a reminder that cybersecurity awareness must start at the management level. Without consistent backing, even the most essential technical improvements will struggle to gain traction in a resistant workplace. By prioritizing a robust password policy, the school finally secured its digital perimeter against future threats.
Password Policy Market Impact and Industry Significance
The introduction of Password Policy represents a pivotal shift in modern technological adoption across enterprise and consumer sectors alike. Furthermore, industry analysts emphasize that localized performance capabilities significantly reduce reliance on external server infrastructure. Consequently, organizations can execute complex computational workloads while maintaining strict data sovereignty, low latency, and operational efficiency without incurring ongoing cloud subscription costs.
Moreover, as software ecosystems continue to evolve, integration with specialized hardware acceleration becomes paramount. Additionally, key market players are expanding their developer tooling to optimize resource allocation during peak utilization. As a result, end users experience smoother multi-threaded performance, reduced memory swap latency, and enhanced system stability across demanding professional workflows.
Performance Benchmarks and Practical Password Policy Scenarios
In real-world deployment scenarios, evaluating sustained throughput and thermal efficiency is essential for technical decision-makers. Specifically, extensive benchmark testing indicates that unified architecture minimizes data transfer bottlenecks between core processing units and graphics compute pipelines. Therefore, demanding tasks operate with minimal compute overhead.
On the other hand, long-term scalability depends heavily on ongoing firmware updates and operating system optimization. Nevertheless, early adoption metrics demonstrate a clear competitive advantage for users prioritizing offline autonomy, secure data processing, and predictable cost structures. Ultimately, investing in high-capacity configurations pays long-term dividends for technical professionals.
